
 Join us on Discord








Is the Lovable .env file safe on GitHub?
Lovable keeps the .env file in your GitHub repository on purpose. Everyone who can see the repository can read it. That is fine for what Lovable puts there. It is not fine for secret keys.
What is in the file
The address, the public key and the project ID of your Supabase backend: VITE_SUPABASE_URL, VITE_SUPABASE_PUBLISHABLE_KEY and VITE_SUPABASE_PROJECT_ID. Apps made since May 2026 also have the same three names without VITE_.
Why that is fine
Values that start with VITE_ are built into the code the browser downloads. Anyone who opens your app can read them. Lovable's docs say the same: they are safe to be public.
Do not add .env to .gitignore. Lovable's docs say it needs the file in the repository to build the preview. Vercel, Cloudflare and PanelAlpha build from GitHub too, and read the Supabase values from the same file.
What must never be in it
- The service_role key of Supabase. It skips the access rules of your database.
- Stripe secret keys and webhook secrets.
- AI provider keys, like OPENAI_API_KEY.
These belong in the secrets of the backend. While you build in Lovable, that is Secrets in Lovable. With your own Supabase project, it is Edge Functions, Secrets in the Supabase dashboard.
Check your file in one prompt
Paste this into Claude Code, Codex or Cursor in the project folder:
Check the .env file. Tell me in two short lines if it holds anything that is not public, like a service_role key or a Stripe secret key. Do not print any value.
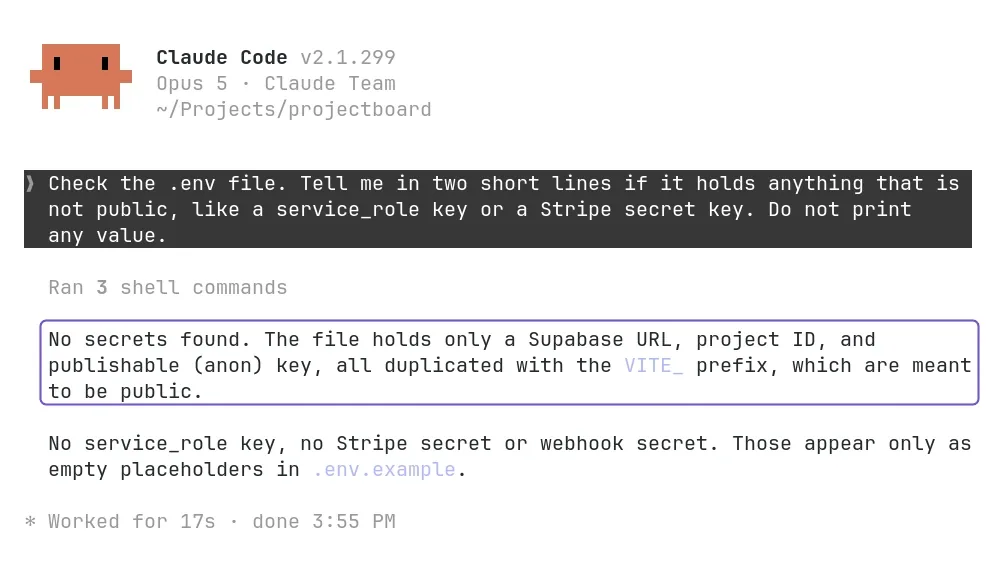
Read what the tool answers. You should see that the file holds only public values.
If a secret was in it
Removing it from the file is not enough. It stays in the Git history of the repository. Create a new key at the provider, delete the old one and put the new one in the backend secrets.